
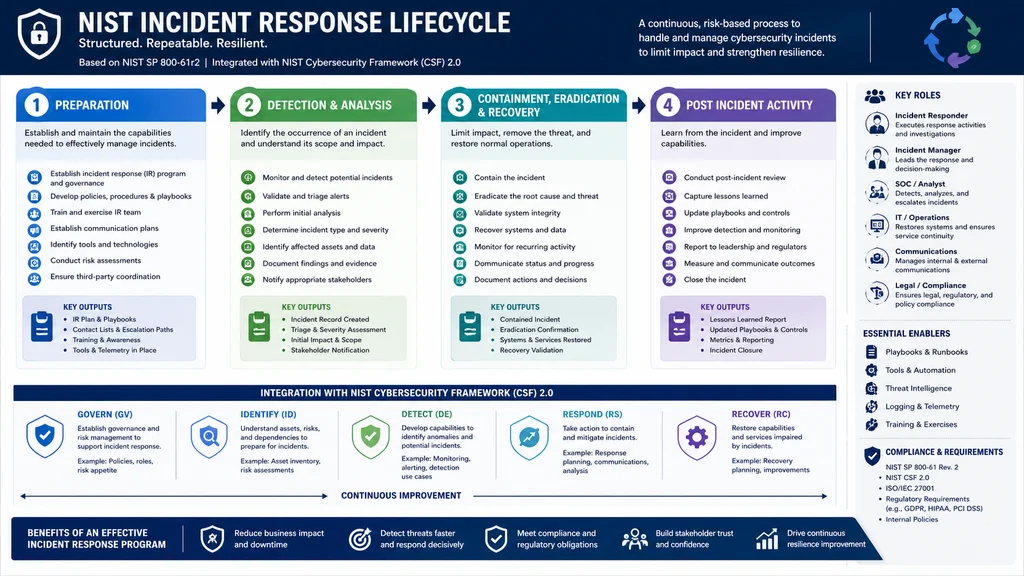
A NIST incident response plan template provides a structured framework based on the NIST SP 800 61 guidelines for handling cybersecurity incidents. It covers the four key phases: Preparation, Detection and Analysis, Containment/Eradication/Recovery, and Post Incident Activity. Top alternatives: NIST SP 800 61 IR template, Incident response playbook framework, Cybersecurity incident plan, Computer security incident handling guide, and CSF 2.0 incident response template.
We all hope it won’t happen to us. But when the moment comes, having a solid incident response plan can mean the difference between a quick recovery and a full blown crisis. Whether you’re a small business owner, a cybersecurity professional, or an IT manager, being prepared isn’t just smart, it’s essential.
- Think about it. When a security incident hits, those first few minutes matter most. The teams who have a plan know exactly what to do. They don’t freeze. They don’t waste precious time figuring things out. They just act.
And here’s the thing, a NIST incident response plan template isn’t just about having a document on a shelf. It’s about creating a system that everyone understands, practices, and can execute without thinking. The National Institute of Standards and Technology (NIST) recently updated its guidance with SP 800 61 Revision 3, aligning it with the Cybersecurity Framework (CSF) 2.0 to help organizations manage incidents as part of overall risk management . This isn’t just about reacting anymore, it’s about planning in a smart, structured way.
NIST Framework Overview Responses
1. NIST SP 800 61 Rev 3 aligns incident response with CSF 2.0 core functions
Example: Use this when explaining the foundational structure of NIST’s approach.
Meaning: The latest guidance integrates incident response with Govern, Identify, Protect, Detect, Respond, and Recover functions .
2. The updated NIST lifecycle emphasizes continuous improvement over a fixed loop
Example: Use this when discussing how incident response has evolved.
Meaning: The new model focuses on constant threat detection, clear roles, and ongoing integration with business continuity teams .
3. NIST breaks the incident response process into four key phases
Example: Use this when teaching the fundamental NIST framework.
Meaning: The phases are Preparation, Detection and Analysis, Containment/Eradication/Recovery, and Post Incident Activity .
4. The framework provides a repeatable roadmap for handling security threats
Example: Use this when justifying why organizations should adopt NIST standards.
Meaning: It gives teams a structured way to respond to incidents of any size .
5. NIST emphasizes integration with enterprise risk management (ERM)
Example: Use this when connecting IR to broader business strategy.
Meaning: The updated guidance requires closer coordination between technical teams and business leaders .
6. The CSF 2.0 Community Profile outlines prioritized outcomes for incident handling
Example: Use this when customizing NIST guidance for your organization.
Meaning: Each CSF activity is rated High, Medium, or Low priority for incident response .
7. NIST SP 800 61r3 was released in April 2025 as a long awaited update
Example: Use this when discussing the current state of NIST guidance.
Meaning: The update followed the February 2024 release of CSF 2.0 .
8. The new guidance helps organizations manage incidents as part of overall risk management
Example: Use this when explaining why NIST matters for business leaders.
Meaning: It moves incident response from a reactive activity to a strategic risk management function .
9. NIST defines roles for internal teams and outside partners in incident response
Example: Use this when building your response team structure.
Meaning: Clear role definition is a central emphasis in the updated guidance .
10. The framework encourages organizations to treat every incident as a learning opportunity
Example: Use this when promoting a continuous improvement culture.
Meaning: Post incident reviews should feed back into training, procedures, and playbooks .
11. NIST’s phased approach helps limit damage and recover quickly
Example: Use this when justifying the framework to leadership.
Meaning: The structured lifecycle helps teams respond effectively to cybersecurity incidents .
12. The updated guidance uses six CSF functions to shape how organizations handle incidents
Example: Use this when mapping NIST guidance to your security program.
Meaning: Govern, Identify, Protect, Detect, Respond, and Recover are the six core functions .
Preparation Phase Responses
1. Define scope, objectives, and severity classifications before any incident
Example: Use this when starting your incident response planning.
Meaning: Your plan must define incidents, escalation paths, and out of band communications upfront .
2. Use a four tier severity scale for incident classification
Example: Use this when setting up your incident prioritization system.
Meaning: SEV 1 (critical), SEV 2 (major), SEV 3 (moderate), and SEV 4 (low) help teams prioritize effectively .
3. Assemble your incident response team with clear leadership roles
Example: Use this when building your CSIRT structure.
Meaning: Essential roles include Incident Commander and Technical Lead .
4. Pre negotiate at least one external IR retainer before you need it
Example: Use this for surge capacity planning.
Meaning: Negotiating a contract during an active SEV 1 costs time you don’t have .
5. Develop and maintain an accurate asset inventory
Example: Use this when identifying critical infrastructure.
Meaning: You need to know your cloud accounts, IAM roles, Kubernetes clusters, and data stores .
6. Audit your log coverage before an incident starts
Example: Use this when preparing detection capabilities.
Meaning: The gap is frequently detection rules, not data collection .
7. Create scenario specific response playbooks for common attack types
Example: Use this when developing response procedures.
Meaning: Build playbooks for cloud credential compromise, cloud storage exposure, container compromise, and ransomware .
8. Establish communication and escalation protocols that work without manual coordination
Example: Use this when designing your alert workflow.
Meaning: Alert fires to on call analyst, triaged, and escalated based on severity .
9. Pre identify contacts for your local FBI field office and cloud provider
Example: Use this when preparing external communications.
Meaning: Contact information should be stored in your IRP, not searched for during a breach .
10. Build detection rules that support your IR workflows
Example: Use this when developing detection capabilities.
Meaning: Each rule needs MITRE ATT&CK mapping, default severity, linked playbook URL, and containment actions .
11. Involve Legal, HR, Privacy, Communications, and Executive Leadership in planning
Example: Use this when developing a comprehensive IR plan.
Meaning: These teams should be actively involved in planning and response activities .
12. Create a RACI matrix to define who does what during an incident
Example: Use this when assigning roles and responsibilities.
Meaning: Document who is Responsible, Accountable, Consulted, and Informed for each activity .
Detection and Analysis Responses
1. Use multiple detection sources to identify potential incidents
Example: Use this when setting up monitoring capabilities.
Meaning: Sources include SIEM logs, threat intelligence, network monitoring, and third party services .
2. One source equals investigate, two sources equals incident, three sources equals all hands
Example: Use this as a rule of thumb for validation.
Meaning: This approach prevents both alert fatigue and dangerous delays .
3. Conduct initial assessment in the first five minutes of an alert
Example: Use this when training your on call team.
Meaning: Answer key questions: Can customers complete critical operations right now? What changed in the last 2 hours?
4. Document your assessment immediately using a Slack thread or incident platform
Example: Use this when starting an incident log.
Meaning: Don’t rely on memory; this becomes your incident timeline .
5. Use pre written notification templates for different severity levels
Example: Use this when preparing communication materials.
Meaning: During an incident, you don’t have time to craft perfect prose .
6. Trust customer reports over monitoring alerts in some cases
Example: Use this when validating detection sources.
Meaning: If three customers say they can’t complete a transaction, that’s SEV 1 even if monitoring looks fine .
7. Detect quickly using SIEMs, logs, and threat intelligence
Example: Use this when implementing detection tools.
Meaning: Monitor your networks, systems, people, and third party services .
8. Prioritize human triage quality over automated detection speed
Example: Use this when building a realistic detection strategy.
Meaning: AI reduces mean time to detect, but analysts make confirmation decisions that trigger regulatory clocks .
9. Validate alerts against known issues and documented fixes
Example: Use this in the analysis process.
Meaning: Check incident history and runbooks before starting from scratch .
10. Define severity tiers in the plan itself, not during an incident
Example: Use this when setting up incident classification.
Meaning: Low, Medium, and High tiers with specific handling requirements .
11. Establish who can declare an incident and set severity
Example: Use this when defining authorization levels.
Meaning: Clear escalation paths prevent confusion during a live event .
12. Track MTTD (Mean Time to Detect) as a primary metric
Example: Use this when measuring detection effectiveness.
Meaning: This figure informs security investment decisions more reliably than incident counts alone .
Containment Responses
1. Target containment actions under 30 minutes for SEV 1 incidents
Example: Use this when setting response time objectives.
Meaning: Speed is critical for critical incidents .
2. Route around the failure if you have backup systems available
Example: Use this when planning workaround strategies.
Meaning: Switch to backup processors or systems even if they cost more .
3. Implement emergency rollback if changes were made in the last four hours
Example: Use this for change related incidents.
Meaning: Rollback immediately, validate, then investigate why the change caused the issue .
4. Isolate affected systems to prevent lateral movement
Example: Use this in containment procedures.
Meaning: In a zero trust environment, containment causes less operational disruption .
5. Image the disk before deleting malware
Example: Use this in evidence preservation.
Meaning: Never skip short term containment in the rush to eradicate; deleting malware before imaging destroys evidence for forensics or insurance claims .
6. Disable problematic features sitewide temporarily
Example: Use this for applicationspecific incidents.
Meaning: If product recommendations are crashing pages, disable them temporarily .
7. Implement geographic or device based isolation when applicable
Example: Use this for targeted issues.
Meaning: If mobile checkout is broken but desktop works, route mobile users to a simplified checkout .
8. Throttle traffic if necessary during DDoS attacks
Example: Use this for denial of service incidents.
Meaning: Implement rate limiting to keep the site usable for some customers .
9. Use cloud native containment capabilities when available
Example: Use this for cloud based incidents.
Meaning: Isolate affected resources, revoke suspicious IAM sessions, or isolate compromised containers .
10. Check if a thirdb party service is degraded before spending time on internal investigation
Example: Use this in the containment decision tree.
Meaning: Implement fallback (cached data, simplified flow, alternative provider) and document for vendor SLA claims .
11. Document containment actions as part of your incident timeline
Example: Use this for legal and compliance purposes.
Meaning: Treat your incident decision log as a legal document from the moment you open it .
12. Ensure your containment strategy reflects your organization’s risk appetite
Example: Use this when developing containment procedures.
Meaning: If your organization has low tolerance for downtime, prioritize rapid containment over forensic preservation .
Eradication Responses
1. Remove the root cause of the incident completely
Example: Use this when moving from containment to eradication.
Meaning: Remove malware, unauthorized accounts, and exploited vulnerabilities .
2. Restore systems from clean, verified backups
Example: Use this for recovery planning.
Meaning: Use backups to restore services after eradication .
3. Monitor restored systems to confirm the attacker hasn’t regained access
Example: Use this after recovery actions.
Meaning: Enhanced monitoring during the 48 hour period after recovery is recommended .
4. Apply patches to address exploited vulnerabilities
Example: Use this for vulnerability based incidents.
Meaning: Ensure the root cause is eliminated permanently .
5. Rotate credentials that may have been compromised
Example: Use this after credential based incidents.
Meaning: Change passwords, API keys, and access tokens .
6. Update detection rules based on what you learned
Example: Use this to improve future detection.
Meaning: Use the incident to strengthen your security posture .
7. Perform a thorough investigation of how the incident occurred
Example: Use this in the analysis process.
Meaning: Understand the attack vector to prevent recurrence .
8. Document all eradication actions for compliance and improvement
Example: Use this for record keeping.
Meaning: A full record helps with post incident review and regulatory reporting .
9. Validate that eradication was successful before ending the incident
Example: Use this when transitioning to post incident activity.
Meaning: Confirm the threat is completely removed .
10. Coordinate with legal and compliance teams during eradication
Example: Use this when regulatory reporting is required.
Meaning: Evidence handling must be documented for potential investigations .
11. Use the incident to build or update specific playbooks
Example: Use this for continuous improvement.
Meaning: Each playbook should be reviewed after every relevant incident .
12. Share eradication lessons with your broader security team
Example: Use this for team learning.
Meaning: Cross training helps build organizational capability .
Recovery Responses
1. Restore systems and services to normal operation
Example: Use this when completing the incident response lifecycle.
Meaning: The recovery phase brings systems back online .
2. Implement enhanced monitoring for 48 hours after recovery
Example: Use this to ensure the attacker hasn’t returned.
Meaning: Monitor for signs of re compromise .
3. Validate that restored systems are functioning correctly
Example: Use this for quality assurance.
Meaning: Test systems before full restoration .
4. Follow your business continuity procedures during recovery
Example: Use this for maintaining operations.
Meaning: Minimize operational disruption .
5. Communicate recovery status to stakeholders and leadership
Example: Use this for managing expectations.
Meaning: Keep everyone informed as systems come back online .
6. Document recovery actions and results
Example: Use this for compliance and future reference.
Meaning: A complete record helps with post incident improvement .
7. Verify data integrity after restoration
Example: Use this for data dependent systems.
Meaning: Ensure data wasn’t corrupted or lost .
8. Implement any needed system hardening based on lessons learned
Example: Use this for improving security posture.
Meaning: Strengthen defenses where they were weak .
9. Coordinate with business units to confirm operational readiness
Example: Use this for business continuity.
Meaning: Ensure all teams are ready to resume normal operations .
10. Update your incident response plan based on recovery lessons
Example: Use this for plan maintenance.
Meaning: Use the experience to improve your plan .
11. Consider the recovery timeline in your incident metrics
Example: Use this for measuring effectiveness.
Meaning: Track time to recover as a key performance indicator .
12. Document the business impact of the incident for future risk assessment
Example: Use this for enterprise risk management.
Meaning: Understand the real world consequences of the event .
Post Incident Activity Responses
1. Conduct a lessons learned review within one to two weeks of closure
Example: Use this for post incident analysis.
Meaning: A short review while details are fresh .
2. Don’t point fingers; focus on honest questions about what happened
Example: Use this when setting review culture.
Meaning: What went well, what didn’t, and what caused delays .
3. Feed lessons learned back into training programs
Example: Use this for continuous improvement.
Meaning: Use insights to better prepare teams for the next incident .
4. Update your procedures and playbooks based on what you learned
Example: Use this for plan maintenance.
Meaning: An outdated plan won’t help during the next real world event .
5. Track MTTR (Mean Time to Respond) as a key metric
Example: Use this for measuring response effectiveness.
Meaning: This metric helps inform security investment decisions .
6. Document post incident findings for regulatory compliance
Example: Use this when regulators require information.
Meaning: Some incidents require formal reporting .
7. Share insights with your broader industry when appropriate
Example: Use this for community improvement.
Meaning: Threat intelligence sharing strengthens the entire ecosystem .
8. Integrate IR metrics into board level risk reporting
Example: Use this for leadership visibility.
Meaning: When leadership sees MTTD trends alongside financial exposure, investment decisions improve .
9. Conduct a full forensic investigation if required
Example: Use this for legal or insurance purposes.
Meaning: Evidence preservation standards and chain of custody requirements may apply .
10. Notify affected parties as required by law
Example: Use this for data breach incidents.
Meaning: Know your regulatory notification obligations, such as the 6 hour CERT In reporting window .
11. Review your detection rules and improve them
Example: Use this for detection enhancement.
Meaning: Use the incident to make detection faster next time .
12. Maintain a living playbook library covering ransomware, insider threat, data exfiltration, and supply chain compromise
Example: Use this for ongoing preparedness.
Meaning: Each playbook should be reviewed after every relevant incident .
Role and Responsibility Responses
1. Designate an Incident Commander who leads response and makes critical decisions
Example: Use this when assigning leadership roles.
Meaning: Clear leadership is essential during a crisis .
2. Appoint a Technical Lead who investigates, contains, and eradicates
Example: Use this for technical role assignment.
Meaning: This person leads the technical response .
3. Assign a Communications Lead to manage internal and external messaging
Example: Use this for communication planning.
Meaning: One designated spokesperson ensures consistent information .
4. Include Legal in your response team to assess regulatory obligations
Example: Use this when regulatory compliance matters.
Meaning: Legal advises on notification requirements and reporting timelines .
5. Involve HR if the incident involves internal employees
Example: Use this when personnel matters arise.
Meaning: HR must be engaged if staff operations are impacted .
6. Include Privacy teams to evaluate whether personal data was involved
Example: Use this for data protection compliance.
Meaning: Privacy teams determine whether regulatory bodies need notification .
7. Ensure Executive Leadership is involved for big picture decisions
Example: Use this for board level engagement.
Meaning: Leadership approves major response actions and stakeholder notifications .
8. Use a RACI matrix to define who does what
Example: Use this when assigning responsibilities.
Meaning: Responsible, Accountable, Consulted, and Informed roles for each activity .
9. Define who can pull a system offline without waiting for approval
Example: Use this for authorization planning.
Meaning: This prevents delays when an executive is unavailable .
10. Identify who is authorized to communicate with regulators
Example: Use this for external communication planning.
Meaning: Clear authority prevents conflicting statements .
11. Document external IR partner roles in your response plan
Example: Use this for third party coordination.
Meaning: Know what your external partner will and won’t do .
12. Review roles regularly and update them as people change positions
Example: Use this for plan maintenance.
Meaning: Keep the plan current with personnel changes .
Communication Responses
1. Use a single approved communication channel for incident updates
Example: Use this for internal communication.
Meaning: One channel prevents scattered information .
2. Move internal communication about an active incident to an out of band channel
Example: Use this when the primary system might be compromised.
Meaning: Avoid tipping off attackers who may still have access .
3. Designate one spokesperson for customer, partner, and regulator communications
Example: Use this for external communication.
Meaning: Consistent information prevents confusion .
4. Use pre written notification templates to save time during an incident
Example: Use this when preparing communication materials.
Meaning: You don’t have time to craft perfect prose during a crisis .
5. Document all communications for accountability and legal purposes
Example: Use this for record keeping.
Meaning: A complete record supports post incident review .
6. Know your regulatory reporting timelines in advance
Example: Use this for compliance planning.
Meaning: CERT In requires reporting within 6 hours of noticing an incident .
7. Report what’s known within the reporting window and file supplementary detail afterward
Example: Use this when you don’t have the full picture yet.
Meaning: Don’t delay reporting until you have a complete investigation .
8. Define external communication protocols before an incident
Example: Use this for external messaging planning.
Meaning: Pre defined protocols prevent scrambling when time is critical .
9. Communicate status updates to the board and stakeholders regularly
Example: Use this for leadership engagement.
Meaning: Keep leadership informed during extended incidents .
10. Consider status page updates for customer facing incidents
Example: Use this for customer communication.
Meaning: Proactive communication builds trust with customers .
11. Use social media for broad customer communications when appropriate
Example: Use this for reaching wider audiences.
Meaning: Social media can quickly inform large groups of customers .
12. Coordinate with PR and communications teams on messaging
Example: Use this for public relations.
Meaning: Align messaging with your organization’s communication strategy .
Playbook Development Responses
1. Build playbooks in priority order based on cloud native threat prevalence
Example: Use this when developing playbook strategies.
Meaning: Start with cloud credential compromise, then cloud storage exposure, container compromise .
2. Include triage steps in each playbook
Example: Use this for playbook structure.
Meaning: Clear first steps guide the responder .
3. Specify containment actions with target times in each playbook
Example: Use this for playbook accuracy.
Meaning: Target under 30 minutes for SEV 1 incidents .
4. Include investigation procedures with named log sources
Example: Use this for playbook completeness.
Meaning: Tell responders exactly where to look .
5. Define eradication steps clearly in each playbook
Example: Use this for playbook structure.
Meaning: Guide responders through the fix .
6. Include recovery verification steps
Example: Use this for playbook completeness.
Meaning: Confirm systems are actually fixed .
7. Add a 48 hour enhanced monitoring period after recovery
Example: Use this for playbook completeness.
Meaning: Watch for signs of re compromise .
8. Assign ownership to roles, not individuals
Example: Use this for playbook sustainability.
Meaning: The plan works even if specific people leave .
9. Review playbooks after every relevant incident
Example: Use this for playbook maintenance.
Meaning: Keep playbooks current with lessons learned .
10. Test playbooks through tabletop exercises
Example: Use this for playbook validation.
Meaning: Exercises expose gaps in your plan .
11. Store playbooks in an accessible location
Example: Use this for playbook accessibility.
Meaning: The plan is only useful if people can find it .
12. Link playbooks to detection rules for seamless response
Example: Use this for playbook integration.
Meaning: Detection rules should include the playbook URL .
Testing and Exercise Responses
1. Run quarterly full tabletop exercises for two to three hours
Example: Use this for comprehensive exercise planning.
Meaning: Regular exercises test whether the team can execute the plan under pressure .
2. Conduct monthly 15 minute scenario inject drills
Example: Use this for frequent practice.
Meaning: Short drills keep skills fresh .
3. Include unannounced drills to test real readiness
Example: Use this when you want an honest assessment.
Meaning: Simulates real emergency conditions more accurately .
4. Use cloud native injects for relevant testing
Example: Use this for cloudbased exercises.
Meaning: Test the scenarios you’re most likely to face .
5. Document exercise results and identified gaps
Example: Use this for exercise evaluation.
Meaning: Create a record for continuous improvement .
6. Tabletop exercises are one of the highest value activities for small teams
Example: Use this when justifying exercise investment.
Meaning: They expose gaps without the cost of a real incident .
7. Run joint tabletop exercises with operational teams for OT environments
Example: Use this for industrial control systems.
Meaning: Gaps found will be procedural and communicative, not just technical .
8. Test different emergency scenarios during training exercises
Example: Use this when you need comprehensive readiness.
Meaning: Broadens your team’s preparedness .
9. Use the CIS tabletop guide for scenario templates
Example: Use this when you need starting points.
Meaning: External templates provide structure for your exercises .
10. Practice containment scenarios specifically
Example: Use this for focused exercise planning.
Meaning: Test your ability to contain quickly .
11. Include communication exercises in your drills
Example: Use this for testing communication protocols.
Meaning: Test your notification and escalation procedures .
12. Review and update exercises based on past incidents
Example: Use this for exercise improvement.
Meaning: Use real experiences to make exercises more realistic .
Evidence and Documentation Responses
1. Treat your incident decision log as a legal document from the moment you open it
Example: Use this for documentation discipline.
Meaning: Courts and regulators will read it exactly that way .
2. Preserve evidence according to chain of custody standards
Example: Use this for evidence handling.
Meaning: Sloppy documentation at the containment stage can undermine a prosecution or defense later .
3. Document all response actions in real time
Example: Use this for incident logging.
Meaning: Don’t rely on memory; create a timeline as you go .
4. Image disks before deleting malware or data
Example: Use this for evidence preservation.
Meaning: Deleting malware before imaging destroys evidence for forensics or insurance claims .
5. Maintain logs for the required retention period
Example: Use this for compliance.
Meaning: CERT In requires log retention for 180 days .
6. Record the date, time, and participants in every response action
Example: Use this for documentation discipline.
Meaning: Complete records support investigation and compliance .
7. Document all communication decisions and messages
Example: Use this for accountability.
Meaning: Know who said what and when .
8. Understand which logs you own and which your cloud provider retains
Example: Use this for cloud based response.
Meaning: Shared responsibility models mean you may not have access to all logs .
9. Use standardized forms for incident documentation
Example: Use this for consistency.
Meaning: Standard forms ensure you capture all necessary information .
10. Preserve evidence for potential insurance claims
Example: Use this for financial protection.
Meaning: Good documentation supports insurance claims .
11. Document lessons learned for compliance and improvement
Example: Use this for post incident activity.
Meaning: A complete record helps with regulatory reporting and plan updates .
12. Ensure documentation is accessible to your legal team
Example: Use this for legal coordination.
Meaning: Legal may need access for regulatory responses .
Legal and Compliance Responses
1. Know your regulatory reporting obligations before an incident
Example: Use this for compliance planning.
Meaning: CERT In requires reporting within 6 hours of noticing an incident in India .
2. Report what’s known within the window; file supplementary detail later
Example: Use this when you don’t have the full picture.
Meaning: Don’t delay reporting while you investigate .
3. Coordinate with legal teams on notification requirements
Example: Use this when legal involvement is required.
Meaning: Legal advises on regulatory and contractual obligations .
4. Consider DORA requirements for financial services firms
Example: Use this for financial sector compliance.
Meaning: DORA mandates ICT incident classification, reporting, and resilience testing .
5. Align incident response with GDPR breach notification requirements
Example: Use this for data protection compliance.
Meaning: Know when personal data breaches require notification .
6. Involve HR for incidents involving internal employees
Example: Use this when personnel matters arise.
Meaning: HR must be engaged if staff conduct is involved .
7. Work with privacy teams for incidents involving personal data
Example: Use this for data protection compliance.
Meaning: Privacy teams determine whether regulatory bodies need notification .
8. Document compliance activities for regulatory audits
Example: Use this for audit readiness.
Meaning: Complete records support regulatory reviews .
9. Understand sector specific compliance requirements
Example: Use this for industry specific planning.
Meaning: Healthcare, financial services, and critical infrastructure have unique requirements .
10. Align IR metrics with board level risk reporting
Example: Use this for governance.
Meaning: Tie MTTD and MTTR trends to financial exposure estimates .
11. Use NIST CSF as a framework for demonstrating compliance
Example: Use this for compliance strategy.
Meaning: The CSF is recognized as a leading standard by regulators .
12. Coordinate with law enforcement when required
Example: Use this for serious incidents.
Meaning: Some incidents require FBI or local law enforcement notification .
FAQs
What is a NIST incident response plan template?
A NIST incident response plan template is a structured document based on the NIST SP 800 61 guidelines that provides a framework for preparing for, detecting, responding to, and recovering from cybersecurity incidents. It covers the four key phases: Preparation, Detection and Analysis, Containment/Eradication/Recovery, and Post Incident Activity .
Why was NIST SP 800 61 updated?
The updated NIST SP 800 61 Revision 3 was released in April 2025 to align with the Cybersecurity Framework (CSF) 2.0, which was published in February 2024. The update helps organizations manage cybersecurity incidents as part of overall risk management, not just react to them .
What roles should be included in a NIST incident response plan?
A NIST aligned IR plan should include an Incident Commander, Technical Lead, Legal, HR, Privacy, Communications, and Executive Leadership. Each role has specific responsibilities during and after an incident .
How often should I test my incident response plan?
You should run quarterly full tabletop exercises and monthly short scenario drills. Regular testing exposes gaps in your plan without the cost of a real incident .
What are the key phases of the NIST incident response process?
The NIST incident response process has four phases: Preparation, Detection and Analysis, Containment/Eradication/Recovery, and Post Incident Activity. These phases provide a repeatable roadmap for handling cybersecurity incidents .
Conclusion
A NIST incident response plan template is more than a document. It’s a system that protects your organization, preserves trust, and gives you confidence that you can handle whatever comes your way. When you invest time in planning, training, and practicing, you’re building resilience that pays off when it matters most.
The latest NIST guidance, SP 800 61 Revision 3, emphasizes continuous improvement and integration with enterprise risk management . This isn’t just about reacting to incidents anymore, it’s about building a culture of preparedness that spans your entire organization.
Remember, the best plan is one that people actually use. Keep it practical, keep it current, and make sure everyone knows their role. Run drills, learn from them, and keep improving. The more you practice, the more natural your response becomes.
Now is the time to start or review your NIST incident response plan template. Don’t wait until the next security incident to figure out what to do. Be proactive, be prepared, and be confident that you can protect what matters most.
.




5 thoughts on “ 150+ Best NIST Incident Response Plan Template Strategies for 2026”