
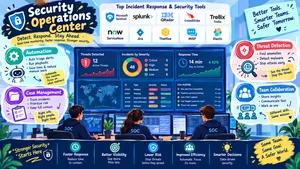
Managed detection and response technology combines 24/7 threat monitoring, expert-led investigation, and rapid incident response to protect organizations from cyber attacks. It delivers enterprise-grade security without the need for an in-house security operations center. Top alternatives: MDR security services, threat hunting platforms, SOC-as-a-service, managed EDR solutions, and extended detection and response systems.Your organization faces cyber threats every single day. Ransomware attacks are getting smarter. Phishing campaigns are harder to spot. And your security team is drowning in thousands of alerts while trying to protect critical data. That’s where managed detection and response technology comes in .
Think of it as having a team of security experts watching your systems around the clock, ready to detect and stop threats before they cause damage. No more waking up to a breach notification. No more worrying about whether your antivirus caught everything. MDR technology gives you peace of mind by combining advanced monitoring tools with human expertise that interprets what’s actually happening in your network .
Whether you’re a growing business without a full security team or an established company looking to strengthen your defenses, understanding managed detection and response technology is your first step toward better cybersecurity. Let’s explore what makes this approach so effective and why organizations everywhere are making the switch.
Core Capability Responses
1. Continuous 24/7 monitoring across all endpoints and networks
Example: Use this when explaining how MDR protects your organization around the clock.
Meaning: Round-the-clock surveillance eliminates time-zone blind spots and ensures threats are caught immediately .
2. Proactive threat hunting for hidden intrusions
Example: Describe this when showing how MDR goes beyond waiting for alerts.
Meaning: Security analysts actively search for sophisticated threats that automated tools might miss .
3. Rapid detection and containment within minutes
Example: Use this when discussing response speed capabilities.
Meaning: MDR providers can isolate infected systems before ransomware spreads .
4. Integration of AI and machine learning for anomaly detection
Example: Mention this when explaining how MDR identifies unknown threats.
Meaning: Behavioral analytics spot deviations from normal patterns that indicate possible attacks .
5. Expert-led investigation and validation of alerts
Example: Use this when discussing how MDR reduces false positives.
Meaning: Human analysts verify threats so your team only responds to genuine incidents .
6. Endpoint, network, cloud, and identity monitoring
Example: Describe this when explaining comprehensive coverage.
Meaning: MDR technology protects all parts of your IT environment, not just endpoints .
7. Automated response actions for high-confidence threats
Example: Use this when showing how MDR stops attacks quickly.
Meaning: Playbooks trigger immediate containment without waiting for human approval .
8. Threat intelligence integration for predictive defense
Example: Mention this when explaining how MDR stays current.
Meaning: Global threat data helps anticipate new attack methods before they strike .
9. Vulnerability context and risk-based prioritization
Example: Use this when discussing how MDR focuses on what matters most.
Meaning: Active exploits are mapped to known vulnerabilities for efficient remediation .
10. Incident management and guided response workflows
Example: Describe this when showing how MDR handles the full incident lifecycle.
Meaning: Providers deliver actionable recommendations and support through every step .
11. Compliance support and audit-ready reporting
Example: Use this when discussing how MDR helps meet regulations.
Meaning: Built-in reporting satisfies GDPR, HIPAA, PCI-DSS, and SOC 2 requirements .
12. Remote forensic investigation and analysis
Example: Mention this when showing how MDR uncovers root causes.
Meaning: Digital forensics capabilities help understand how breaches occurred and prevent recurrence .
Security Challenge Responses
1. Reducing alert fatigue for overwhelmed security teams
Example: Use this when explaining how MDR filters out noise.
Meaning: Providers validate alerts so your team only sees genuine threats, not false positives .
2. Addressing the cybersecurity talent shortage
Example: Mention this when discussing why organizations choose MDR.
Meaning: You gain immediate access to expert analysts without recruitment challenges .
3. Stopping ransomware before encryption completes
Example: Use this when showing MDR’s effectiveness against major threats.
Meaning: Behavioral detection catches attacks using legitimate tools that traditional antivirus misses .
4. Detecting living-off-the-land attack techniques
Example: Describe this when explaining how MDR catches sophisticated threats.
Meaning: Monitoring of PowerShell, WMI, and other trusted tools reveals malicious misuse .
5. Eliminating visibility gaps across hybrid environments
Example: Use this when discussing comprehensive monitoring.
Meaning: MDR covers endpoints, cloud workloads, networks, and identity systems .
6. Preventing lateral movement within networks
Example: Mention this when showing how MDR stops attackers from spreading.
Meaning: Correlation across multiple data sources reveals coordinated attack chains .
7. Reducing mean time to detect from months to minutes
Example: Use this when discussing MDR’s speed advantage.
Meaning: Industry average detection times drop significantly with 24/7 monitoring and analysis .
8. Managing credential misuse and identity-based attacks
Example: Describe this when explaining protection against compromised accounts.
Meaning: Anomaly detection spots unusual login patterns and privilege escalations .
9. Converting capital expenditure to predictable operational costs
Example: Use this when discussing budget advantages.
Meaning: MDR transforms costly in-house SOC investments into manageable monthly services .
10. Protecting against zero-day and unknown threats
Example: Mention this when showing how MDR handles new attack methods.
Meaning: Behavioral analysis detects anomalies even when no signature exists .
11. Providing instant SOC capabilities without hiring
Example: Use this when discussing resource-constrained organizations.
Meaning: Turnkey security operations center functions are delivered immediately .
12. Decoupling IT teams from constant fire-fighting
Example: Describe this when showing how MDR frees internal resources.
Meaning: Internal staff can focus on strategic initiatives instead of chasing alerts .
Technology Comparison Responses
1. MDR vs EDR: Comprehensive protection beyond endpoints
Example: Use this when explaining why MDR offers more than EDR alone.
Meaning: MDR combines EDR technology with human expertise and full-network visibility .
2. MDR vs XDR: Managed expertise with extended visibility
Example: Mention this when discussing advanced detection options.
Meaning: MDR adds human analysis to XDR’s multi-layered detection capabilities .
3. MDR vs SIEM: Actionable response instead of just logs
Example: Use this when comparing traditional and modern approaches.
Meaning: MDR provides actual containment and response, not just alerting .
4. MDR vs MSSP: Proactive hunting instead of reactive monitoring
Example: Describe this when distinguishing security service types.
Meaning: MDR actively searches for threats while MSSPs often just monitor for alerts .
5. MDR as EDR-as-a-Service with expert interpretation
Example: Use this when explaining the managed aspect.
Meaning: You get the power of EDR without needing to learn complex tools yourself .
6. MDR providing turnkey SOC functions remotely
Example: Mention this when discussing service delivery.
Meaning: All security operations center capabilities are delivered without building infrastructure .
7. MDR combining technology stack with skilled analysts
Example: Use this when explaining the complete service.
Meaning: Technology plus human intelligence creates effective threat management .
8. MDR delivering containment at scale across environments
Example: Describe this when showing response capabilities.
Meaning: Firewall rules, access keys, and email campaigns can be blocked enterprise-wide .
9. MDR integrating with existing security tools and workflows
Example: Use this when discussing deployment flexibility.
Meaning: Providers work with current solutions like Microsoft Defender and Okta .
10. MDR enabling co-managed security operations
Example: Mention this when showing partnership options.
Meaning: Organizations can choose full outsourcing or shared responsibility models .
11. MDR providing global threat intelligence integration
Example: Use this when explaining how MDR stays current.
Meaning: Real-time feeds from multiple sources enrich detection and correlation .
12. MDR supporting regulatory compliance frameworks
Example: Describe this when discussing audit readiness.
Meaning: Log retention and structured reporting satisfy compliance requirements .
Business Value Responses
1. Cost savings of 25% or more compared to in-house SOC
Example: Use this when discussing budget benefits.
Meaning: Organizations report significant savings by outsourcing security operations .
2. Improved security posture through expert guidance
Example: Mention this when showing continuous improvement.
Meaning: Providers deliver intelligence about vulnerabilities and fine-tune controls .
3. Business continuity and resilience against attacks
Example: Use this when discussing operational protection.
Meaning: Fast response minimizes damage and downtime from security incidents .
4. Strategic security planning with professional insights
Example: Describe this when showing long-term value.
Meaning: MDR partners help organizations make better security decisions .
5. Resource optimization for internal IT teams
Example: Use this when discussing productivity benefits.
Meaning: Teams reclaim thousands of hours for strategic initiatives instead of security fire-fighting .
6. Scalable security that grows with your organization
Example: Mention this when discussing flexibility.
Meaning: Services adapt as your infrastructure and threat landscape evolve .
7. Access to multidisciplinary security experts
Example: Use this when showing team capabilities.
Meaning: Digital forensics, adversary tactics, and incident response specialists work together .
8. Custom detection engineering for unique environments
Example: Describe this when discussing tailored protection.
Meaning: Rules are built for proprietary applications and sector-specific threats .
9. Reduced dwell time and faster breach containment
Example: Use this when showing incident response effectiveness.
Meaning: Minutes matter when preventing ransomware spread .
10. Improved compliance audit readiness
Example: Mention this when discussing regulatory benefits.
Meaning: Artifacts for continuous monitoring and incident response testing are readily available .
11. Insurance-ready incident reporting and documentation
Example: Use this when showing practical benefits.
Meaning: Reports can be generated for cyber insurance claims after incidents .
12. Reduced false positives and improved alert accuracy
Example: Describe this when explaining operational efficiency.
Meaning: AI-powered analysis delivers 90% faster threat analysis and 80% fewer false positives .
Implementation Considerations Responses
1. Assessment of your current security maturity and needs
Example: Use this when starting an MDR conversation.
Meaning: Understanding your existing capabilities guides appropriate solution selection .
2. Minimum viable telemetry requirements for effective monitoring
Example: Mention this when discussing data collection.
Meaning: Providers need specific data sources to deliver comprehensive protection .
3. Integration with existing endpoint, cloud, and identity solutions
Example: Use this when showing deployment flexibility.
Meaning: MDR works with Microsoft Defender, Okta, AWS, Azure, and other common platforms .
4. Data sovereignty and compliance with regional regulations
Example: Describe this when discussing privacy requirements.
Meaning: Providers offer data residency in multiple jurisdictions to meet requirements .
5. Co-managed vs fully outsourced operating models
Example: Use this when explaining partnership options.
Meaning: Choose the level of involvement that fits your organization’s needs .
6. Service level agreements for response times and coverage
Example: Mention this when discussing service guarantees.
Meaning: SLAs define expected detection and response performance metrics .
7. Threat intelligence sources and integration methods
Example: Use this when explaining how MDR stays informed.
Meaning: Commercial feeds, open-source data, and proprietary telemetry combine for detection .
8. Automated vs analyst-driven response balance
Example: Describe this when showing operational approach.
Meaning: High-confidence threats trigger automation while complex incidents involve experts .
9. Forensic evidence gathering and preservation procedures
Example: Use this when discussing investigation capabilities.
Meaning: Remote forensic services collect evidence for analysis without on-site presence .
10. Post-incident analysis and continuous improvement cycles
Example: Mention this when showing learning capabilities.
Meaning: Each incident sharpens future detection through feedback loops .
11. Customization for industry-specific threat patterns
Example: Use this when discussing tailored protection.
Meaning: Healthcare, retail, manufacturing, and government organizations have unique needs .
12. Monitoring of email, collaboration tools, and IoT devices
Example: Describe this when showing coverage breadth.
Meaning: Protection extends beyond traditional endpoints to modern work environments .
Detection Methodology Responses
1. Signature-based detection for known malicious patterns
Example: Use this when explaining basic threat identification.
Meaning: Matching against databases of known bad files, hashes, and domains .
2. Behavioral analytics for anomaly identification
Example: Mention this when showing how unknown threats are caught.
Meaning: Establishing baselines and identifying deviations from normal patterns .
3. User and entity behavior analytics for insider threats
Example: Use this when discussing detection of compromised accounts.
Meaning: Monitoring authentication, privilege, data access, and network anomalies .
4. Network traffic analysis for command-and-control detection
Example: Describe this when showing how lateral movement is spotted.
Meaning: Identifying unusual outbound destinations and protocols .
5. Cloud workload and SaaS application monitoring
Example: Use this when explaining modern environment protection.
Meaning: Detection across AWS Lambda, Azure Functions, GCP, and Microsoft 365 .
6. Identity and access management data correlation
Example: Mention this when showing how credential misuse is caught.
Meaning: Anomalous logins, privilege changes, and MFA bypass detection .
7. MITRE ATT&CK framework mapping for attack understanding
Example: Use this when explaining threat classification.
Meaning: Observed activity is mapped to known tactics, techniques, and procedures .
8. Indicators of compromise for known threat identification
Example: Describe this when showing how attacks are confirmed.
Meaning: Forensic artifacts like registry keys, domain queries, and file hashes .
9. Hypothesis-driven threat hunting for user-specific targets
Example: Use this when discussing proactive detection.
Meaning: Focusing on users of interest or where privileged data is at risk .
10. Automated alert triage and prioritization
Example: Mention this when showing how noise is filtered.
Meaning: AI-powered analysis validates threats before human review .
11. Cross-layered event correlation for attack chain detection
Example: Use this when explaining comprehensive visibility.
Meaning: Connecting events across endpoints, networks, identity, and cloud .
12. Continuous threat intelligence feed integration
Example: Describe this when showing how MDR stays current.
Meaning: Real-time feeds enrich detection and correlation across all data sources .
Response Capability Responses
1. Immediate endpoint isolation and quarantine
Example: Use this when showing how MDR stops spread.
Meaning: Infected systems are cut off from the network during investigation .
2. Automated playbook execution for common threats
Example: Mention this when explaining response speed.
Meaning: Pre-approved responses for high-confidence incidents happen instantly .
3. Privilege revocation and credential reset
Example: Use this when discussing identity protection.
Meaning: Compromised accounts are disabled through identity provider integrations .
4. Network blocking of command-and-control domains
Example: Describe this when showing how communication is stopped.
Meaning: Malicious IPs and domains are blocked at network defenses .
5. Cloud access key deactivation in AWS, Azure, GCP
Example: Use this when discussing cloud environment protection.
Meaning: Compromised cloud credentials are immediately disabled .
6. Malicious email campaign quarantine
Example: Mention this when showing email protection.
Meaning: Phishing and malware campaigns are blocked across mail systems .
7. Threat containment through temporary firewall rules
Example: Use this when showing network protection.
Meaning: Malicious traffic is blocked through dynamic policy changes .
8. Configuration rollback to secure states
Example: Describe this when showing remediation capabilities.
Meaning: Unauthorized changes can be reversed automatically .
9. Ransomware blocking before encryption starts
Example: Use this when discussing ransomware protection.
Meaning: Behavioral detection stops attacks using legitimate tools .
10. Guided response recommendations for complex incidents
Example: Mention this when showing analyst support.
Meaning: Expert advice on containment and remediation steps .
11. Post-incident validation and confirmation
Example: Use this when showing complete resolution.
Meaning: Systems are verified clean before returning to normal operation .
12. Remote forensic evidence collection for investigation
Example: Describe this when showing root cause analysis.
Meaning: Evidence is gathered without on-site presence .
Post-Incident Analysis Responses
1. Full scope determination of compromise extent
Example: Use this when showing investigation depth.
Meaning: Understanding what was accessed and what damage occurred .
2. Root cause analysis for prevention planning
Example: Mention this when showing continuous improvement.
Meaning: Identifying how attackers gained entry to prevent recurrence .
3. Incident report creation for stakeholders and insurers
Example: Use this when discussing documentation.
Meaning: Comprehensive reports for audits, executives, and insurance claims .
4. Security control improvement recommendations
Example: Describe this when showing long-term value.
Meaning: Specific guidance on closing detected vulnerabilities .
5. Detection tuning based on attack patterns
Example: Use this when showing learning capabilities.
Meaning: Each incident sharpens future detection and response .
6. Vulnerability patching and remediation guidance
Example: Mention this when discussing protective measures.
Meaning: Prioritized actions to prevent similar attacks .
7. Lessons learned documentation for team training
Example: Use this when showing knowledge transfer.
Meaning: Insights shared with internal teams for improvement .
8. Attack technique mapping for future reference
Example: Describe this when using MITRE ATT&CK.
Meaning: Observed methods cataloged for future detection .
9. Risk score updates based on incident experience
Example: Use this when showing threat assessment evolution.
Meaning: Organization’s risk posture is adjusted based on events .
10. Compliance artifact preservation for audits
Example: Mention this when discussing regulatory needs.
Meaning: Evidence of response and resolution for auditors .
11. Process improvement identification for response workflows
Example: Use this when showing operational refinement.
Meaning: Procedures are updated based on incident experience .
12. Security awareness training recommendations
Example: Describe this when showing human element improvement.
Meaning: Targeted training based on how attacks occurred .
AI and Automation Responses
1. AI-powered threat analysis for faster detection
Example: Use this when explaining modern MDR capabilities.
Meaning: Machine learning processes 60TB daily for instant threat identification .
2. Automated alert triage and validation
Example: Mention this when showing reduced analyst workload.
Meaning: AI filters false positives before human review .
3. Agentic AI for autonomous threat containment
Example: Use this when discussing advanced capabilities.
Meaning: AI systems execute response actions without human intervention .
4. Machine learning for behavior baseline establishment
Example: Describe this when showing how anomalies are spotted.
Meaning: Learning normal patterns for each environment and user .
5. Automated playbook optimization through AI
Example: Use this when showing continuous improvement.
Meaning: Response procedures are refined based on experience .
6. Natural language processing for log analysis
Example: Mention this when explaining data processing.
Meaning: SQL query generation and alert summarization through AI .
7. Automated response workflows for high-confidence threats
Example: Use this when showing speed advantages.
Meaning: Containment happens within minutes without waiting for analysts .
8. Predictive threat modeling and simulation
Example: Describe this when showing proactive capabilities.
Meaning: AI simulates potential attacks to identify vulnerabilities .
9. Intelligent false positive reduction
Example: Use this when discussing operational efficiency.
Meaning: AI reduces false positives by up to 80% .
10. Human-in-the-loop for complex or uncertain incidents
Example: Mention this when showing balanced approach.
Meaning: AI handles simple threats, analysts manage complex cases .
11. Continuous learning from analyst decisions
Example: Use this when showing improvement cycles.
Meaning: AI improves based on how analysts handle incidents .
12. Autonomous investigation of all alerts regardless of priority
Example: Describe this when showing comprehensive coverage.
Meaning: Every alert is assessed within two minutes on average .
Provider Selection Responses
1. Evaluating provider expertise and threat intelligence depth
Example: Use this when starting vendor research.
Meaning: Understanding the team’s experience and global intelligence sources .
2. Reviewing technology stack and integration capabilities
Example: Mention this when assessing compatibility.
Meaning: Ensuring existing security tools can work with the MDR provider .
3. Understanding data collection and retention policies
Example: Use this when discussing privacy concerns.
Meaning: Knowing what data is collected, stored, and how it’s protected .
4. Assessing custom detection engineering capabilities
Example: Describe this when discussing unique environments.
Meaning: Ability to build rules for proprietary applications .
5. Evaluating service level agreements and response commitments
Example: Use this when setting expectations.
Meaning: Clear metrics for detection and response performance .
6. Understanding threat hunting frequency and approach
Example: Mention this when discussing proactive protection.
Meaning: Regular manual hunting for hidden or sophisticated threats .
7. Reviewing regulatory compliance and reporting support
Example: Use this when discussing framework requirements.
Meaning: Alignment with GDPR, HIPAA, PCI-DSS, and SOC 2 .
8. Assessing scalability for organizational growth
Example: Describe this when showing long-term fit.
Meaning: Ability to handle increasing data volumes and complexity .
9. Checking incident response and forensic investigation procedures
Example: Use this when discussing breach handling.
Meaning: Clear processes for containment, analysis, and remediation .
10. Evaluating cost structure and ROI expectations
Example: Mention this when making business decisions.
Meaning: Understanding total investment and expected protection value .
11. Reviewing co-management and collaboration options
Example: Use this when discussing partnership style.
Meaning: Options for shared or fully outsourced operations .
12. Assessing industry-specific experience and references
Example: Describe this when seeking relevant expertise.
Meaning: Providers with experience in your sector understand unique threats .
FAQs
What exactly is managed detection and response technology?
Managed detection and response (MDR) is a cybersecurity service that provides 24/7 threat monitoring, detection, investigation, and incident response. It combines technology with human expertise to protect organizations from cyber attacks .
How does MDR differ from antivirus or EDR?
While antivirus catches known threats and EDR monitors endpoints, MDR adds 24/7 human analysis, proactive threat hunting, and full network visibility. It’s a complete security service rather than just a tool .
Is MDR only for large enterprises?
No. MDR is particularly valuable for organizations without resources for an in-house security team. It provides enterprise-level protection at a fraction of the cost .
What gets monitored in an MDR service?
MDR monitors endpoints, networks, cloud workloads, email, collaboration tools, and identity systems. Coverage includes AWS, Azure, Microsoft 365, and other common platforms .
How quickly can MDR respond to threats?
MDR providers can detect and contain threats within minutes. Advanced systems investigate all alerts in under two minutes and respond immediately to high-confidence threats .
Conclusion
Managed detection and response technology has transformed how organizations approach cybersecurity. It provides the protection of a full security operations center without the massive investment in people and infrastructure. The combination of continuous monitoring, expert analysis, and rapid response creates a defense that’s both comprehensive and cost-effective.
What makes MDR truly valuable is how it addresses real-world challenges. It stops the alert fatigue that overwhelms security teams. It fills the talent gap that prevents many organizations from building effective defenses. And it catches sophisticated attacks that traditional tools miss. The result is stronger security, better resource allocation, and peace of mind for business leaders .
As threats continue to evolve, MDR technology evolves with them. AI-powered analysis, automated response, and advanced detection methods are making protection faster and more effective. Organizations that adopt MDR position themselves to stay ahead of attackers while freeing their internal teams to focus on strategic priorities.
Whether you’re exploring MDR for the first time or looking to strengthen your current security posture, understanding these capabilities is your first step toward better protection. Start evaluating providers today and discover how managed detection and response technology can transform your cybersecurity.



5 thoughts on “200 Essential Managed Detection & Response Technology Insights for Modern Cybersecurity For 2026”