
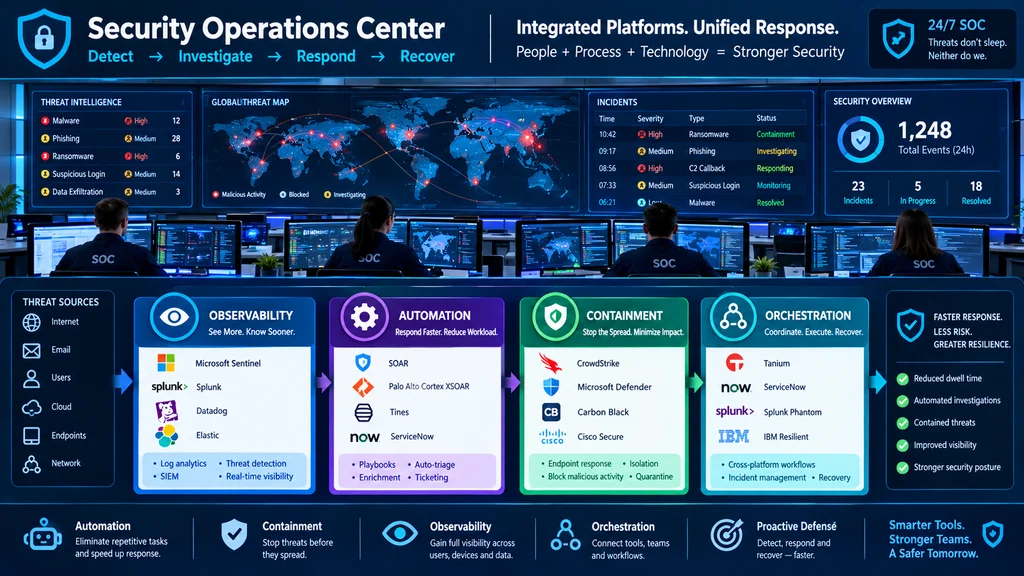
The best incident response platforms in 2026 combine SOAR automation, SIEM correlation, and EDR containment to slash response times from hours to seconds. Top alternatives: Torq, Tines, Cynet 360 AutoXDR, Dynatrace, and KnowBe4 PhishER Plus.
You’re staring at your SIEM dashboard when the alert hits. A suspicious login. Then another. And another. Your heart races, your Slack notifications explode, and suddenly you’re the one who has to coordinate the entire response while everyone else panics.
Sound familiar? If you work in security operations, you know the drill. But here’s the thing: modern incident response platforms have completely changed the game. They’re not just dashboards or ticketing systems. They’re the connective tissue that turns your disconnected security tools into a unified fighting force .
Whether you’re a SOC analyst drowning in alerts, a security engineer building out your stack, or a CISO evaluating vendors, understanding what makes incident response platforms tick is absolutely essential. This guide breaks down 150+ platform capabilities, use cases, and selection criteria to help you build a response capability that actually works when the clock is ticking.
Automation-First Platforms
1. Torq
Example: Use this when you need to automate complex security workflows without writing code.
Meaning: Torq acts as the connective tissue between your detection and response tools, orchestrating actions across your entire stack .
2. Tines
Example: Perfect for security teams that want powerful automation with an intuitive interface.
Meaning: Tines excels at connecting tools and automating workflows, with users praising how fast playbooks execute for containment tasks .
3. Torq Hyperautomation
Example: Use this when you want to reduce MTTR from hours to seconds.
Meaning: Torq’s hyperautomation approach automates everything that can be automated, from Tier-1 triage to containment .
4. Agentless Automation
Example: Ideal when you need to deploy automation in minutes, not months.
Meaning: Torq was built with agentless automation, avoiding the complexity of legacy SOAR tools .
5. No-Code Workflow Builder
Example: Use this when security architects need to build complex flows without engineering resources.
Meaning: Torq’s visual workflow builder lets security teams create automation without waiting for software engineers .
6. API-First Integrations
Example: Essential when you need to ingest alerts from any detection tool.
Meaning: Torq uses API-first integrations to connect with your existing security stack .
7. Automated Phishing Response
Example: Use this when phishing alerts are drowning your SOC team.
Meaning: Torq automatically extracts URLs, checks threat intel, deletes malicious messages, and triggers IAM actions .
8. Coordinated Ransomware Containment
Example: Critical when ransomware is spreading laterally in minutes.
Meaning: Torq can isolate hosts, block traffic, revoke sessions, and open incident tickets automatically .
9. Enrichment and Triage at Scale
Example: Use this when alert fatigue is killing your team’s productivity.
Meaning: Torq automatically enriches alerts with context, reducing false positives and speeding triage .
10. Tines for Containment
Example: Use this when you need fast playbook execution for isolation tasks.
Meaning: Tines users highlight how fast playbooks execute for containment tasks .
11. Cynet 360 AutoXDR
Example: Ideal for organizations that want automated investigation and response in one platform.
Meaning: Cynet combines threat detection, incident response, and automated remediation in a single solution .
12. Cynet Automated Remediation
Example: Use this when you need to eliminate threats across endpoints and networks automatically.
Meaning: Cynet provides automated remediation tools to eliminate malicious presence from your environment .
Observability-Driven Platforms
1. Dynatrace
Example: Use this when you need deep visibility into infrastructure and application performance.
Meaning: Dynatrace provides deep visibility across applications and infrastructure to detect and investigate issues quickly .
2. Dynatrace AI Root Cause Analysis
Example: Perfect when you need to identify the source of incidents without manual troubleshooting.
Meaning: AI-driven root cause analysis helps users pinpoint issues quickly .
3. Datadog
Example: Use this when you need a monitoring-first platform that centralizes alerts.
Meaning: Datadog has a massive market presence and strong footprint in observability and monitoring .
4. Datadog Workflow Triggers
Example: Ideal when you need to trigger workflows fast from monitoring alerts.
Meaning: Datadog is credited for triggering workflows fast and centralizing alerts into action .
5. IBM Instana
Example: Use this for real-time application observability and automated root cause detection.
Meaning: IBM Instana helps teams quickly identify performance issues and infrastructure anomalies .
6. Grafana IRM
Example: Perfect for teams whose dashboards and alerts already live in Grafana.
Meaning: Grafana IRM brings alerting and on-call into the Grafana observability stack .
7. Splunk On-Call
Example: Use this when you want response tightly coupled to Splunk-based monitoring data.
Meaning: Splunk On-Call pairs alerting and on-call with Splunk’s observability and log analytics .
8. Dynatrace for Investigation
Example: Ideal when you need a single pane of glass for monitoring.
Meaning: Dynatrace standardizes visualizations of data across supported technologies .
9. Datadog On-Call
Example: Use this when you want to consolidate observability and response under one roof.
Meaning: Datadog On-Call extends the Datadog platform into paging and escalation .
10. Dynatrace Ease of Use
Example: Great for teams that want an intuitive interface once configured.
Meaning: Dynatrace scores 86% approval for ease of use in G2 reviews .
11. BigPanda AIOps
Example: Use this when you’re drowning in noisy alerts across many monitoring tools.
Meaning: BigPanda correlates and compresses large volumes of alerts into actionable incidents .
12. Better Stack
Example: Perfect for smaller teams that want monitoring and response from a single product.
Meaning: Better Stack bundles uptime monitoring, on-call, and status pages with a quick setup .
Enterprise Orchestration Platforms
1. ServiceNow Security Operations
Example: Use this for enterprise security operations teams that need structured workflows.
Meaning: ServiceNow combines incident response workflows, case management, and integration with IT service management .
2. ServiceNow for Large Enterprises
Example: Ideal when incident response needs to be baked into broader IT processes.
Meaning: ServiceNow Security Operations is commonly used by large organizations .
3. Palo Alto Cortex XSIAM
Example: Use this when you’re already deep in the Palo Alto ecosystem.
Meaning: Cortex XSIAM works best for shops already invested in Palo Alto’s stack .
4. Cortex XSIAM Tight Integration
Example: Perfect when containment benefits come from ecosystem integration.
Meaning: Containment benefits mostly come from tight integration with the rest of Palo Alto’s stack .
5. Jira Service Management
Example: Use this for Atlassian-based ITSM teams that want incident management in their ecosystem.
Meaning: JSM brings incident, problem, and change management into the Atlassian ecosystem .
6. xMatters
Example: Ideal for regulated, audit-heavy enterprises that need compliance-ready records.
Meaning: xMatters focuses on reliable notification, flexible workflows, and audit-ready incident records .
7. Resolver
Example: Use this when you need centralized incident tracking with strong reporting.
Meaning: Resolver offers investigation workflows and reporting for compliance and governance .
8. BreachRx
Example: Perfect for enterprise-wide incident response across legal, privacy, and security teams.
Meaning: BreachRx coordinates the entire response across security, legal, privacy, communications, and executive teams .
9. BreachRx Agentic AI
Example: Use this when you want AI agents that work from live incident context.
Meaning: BreachRx embeds specialized AI agents into live incident workflows while preserving human oversight .
10. ServiceNow Standardized Containment
Example: Ideal when you need to standardize containment across complex environments.
Meaning: ServiceNow helps standardize containment across big, complex environments .
11. Anomali Security Operations Platform
Example: Use this for FedRAMP-compliant security analytics and threat intelligence.
Meaning: Anomali provides SIEM capabilities with incident response workflows and threat intelligence management .
12. Anomali ThreatStream
Example: Perfect when you need automated collection and curation of threat intelligence.
Meaning: ThreatStream provides threat intelligence management with automated IOC deduplication .
Phishing and Email Response Platforms
1. KnowBe4 PhishER/PhishER Plus
Example: Use this when phishing is your main headache and you need quick triage.
Meaning: PhishER is the go-to for phishing response, handling resolution steps quickly .
2. PhishER Strong Reputation
Example: Ideal for organizations where phishing alerts dominate the SOC queue.
Meaning: PhishER has a strong reputation for phishing response .
3. PhishER Quick Resolution
Example: Use this when you need to resolve phishing alerts fast.
Meaning: Reviewers note PhishER handles resolution steps quickly once alerts come in .
4. PhishER for Email Security
Example: Perfect for teams that need to triage user-reported suspicious emails.
Meaning: PhishER specializes in phishing response and email threat analysis .
5. PhishER Market Leader
Example: Use this when you want a proven solution with strong market presence.
Meaning: PhishER/PhishER Plus leads the G2 Incident Response Grid with a 95 score .
6. Automated Phishing Deletion
Example: Use this when you need to delete malicious messages across all inboxes.
Meaning: Torq automatically deletes messages via M365 or Google Workspace API .
7. Phishing URL Extraction
Example: Ideal when you need to automatically extract and check URLs from reported emails.
Meaning: Torq extracts URLs, attachments, and headers for threat intel checks .
8. Phishing Threat Intel Checks
Example: Use this when you need to check reported emails against multiple threat intel sources.
Meaning: Torq checks against Recorded Future, VirusTotal, and other threat intel tools .
9. Phishing IAM Actions
Example: Perfect when a phishing email requires password reset or session revocation.
Meaning: Torq triggers IAM actions like forcing password reset or revoking sessions .
10. Phishing Summary Reports
Example: Use this when you need to post evidence to Slack or Teams for visibility.
Meaning: Torq posts full summaries and evidence to dedicated Slack or Teams channels .
11. Cynet for Phishing Response
Example: Ideal when you want phishing response integrated with broader XDR capabilities.
Meaning: Cynet combines phishing response with automated remediation across the environment .
12. PhishER Plus Advanced Features
Example: Use this when you need advanced phishing analysis beyond basic triage.
Meaning: PhishER Plus offers enhanced capabilities for complex phishing investigations .
Open Source and Budget-Friendly Platforms
1. Wazuh
Example: Use this when you need a free, open-source SIEM with EDR capabilities.
Meaning: Wazuh is completely free and open source with compliance integration .
2. Wazuh Data Sovereignty
Example: Ideal when you need full control over your security data.
Meaning: Wazuh offers total data sovereignty with on-premise deployment .
3. Wazuh Compliance Integration
Example: Perfect for organizations that need CIS, PCI DSS, GDPR, or HIPAA compliance.
Meaning: Wazuh has compliance integration built in .
4. Wazuh FIM
Example: Use this when you need robust file integrity monitoring.
Meaning: Wazuh’s FIM is robust and mature .
5. Elastic Security
Example: Use this when you want an open data model without vendor lock-in.
Meaning: Elastic Security offers an open data model with community-based detection rules .
6. Elastic Self-Hosted
Example: Ideal when you want self-hosted security without license costs.
Meaning: Elastic can be self-hosted without licensing costs under SSPL .
7. Elastic Detection Rules
Example: Perfect for teams that want community-driven detection content.
Meaning: Elastic offers community detection rules and Sigma support .
8. Wazuh Active Community
Example: Use this when you value extensive documentation and community support.
Meaning: Wazuh has an active community with extensive documentation .
9. Squadcast
Example: Use this for budget-friendly alerting, on-call, and runbooks.
Meaning: Squadcast offers SRE-oriented reliability workflows at an accessible price point .
10. Zenduty
Example: Ideal for mid-market teams that want alerting plus playbooks.
Meaning: Zenduty combines alerting and on-call with response playbooks and SLA tracking .
11. Wazuh 5.0 Coming
Example: Use this when planning for future scalability improvements.
Meaning: Wazuh 5.0 is expected in late 2026 with architectural improvements .
12. Cynet for SMBs
Example: Use this when you need an affordable all-in-one platform for smaller teams.
Meaning: Cynet is often considered suitable for smaller organizations .
Containment and Remediation Platforms
1. Cynet Fast Containment
Example: Use this when containment speed is your top priority.
Meaning: Cynet is often mentioned as one of the strongest all-around when it comes to fast containment .
2. Cynet Automated Isolation
Example: Ideal when you need to isolate endpoints automatically.
Meaning: Cynet combines automation, isolation, and threat intel in one place .
3. Torq Fast Containment
Example: Use this when you need to spin up workflows quickly to isolate and respond.
Meaning: Torq is especially praised for how quickly you can spin up workflows to isolate and respond .
4. Tines Fast Containment
Example: Perfect when you need fast playbook execution for containment tasks.
Meaning: Tines users highlight how fast playbooks execute for containment .
5. CrowdStrike Falcon
Example: Use this when you need enterprise-wide visibility and threat intelligence.
Meaning: CrowdStrike offers proactive incident response services to stop active breaches .
6. CrowdStrike Real-Time Response
Example: Ideal when you need immediate threat visibility and adversary ejection.
Meaning: CrowdStrike provides real-time response capabilities with AI-led investigation .
7. SentinelOne Singularity
Example: Use this when you want automatic attack chain reconstruction.
Meaning: SentinelOne’s Storyline automatically reconstructs the complete attack chain .
8. SentinelOne Rollback
Example: Perfect for ransomware recovery with VSS snapshot rollback.
Meaning: SentinelOne offers ransomware rollback based on VSS snapshots .
9. Sophos Intercept X
Example: Use this when you need comprehensive threat analysis and remote response.
Meaning: Sophos Intercept X identifies active threats and launches full-scale response activities .
10. Trend Micro Smart Protection
Example: Ideal when you need to collect data from endpoints, networks, and cloud.
Meaning: Trend Micro collects activity data from multiple sources for comprehensive incident views .
11. Palo Alto Cortex XDR
Example: Use this when you need native correlation with firewall data.
Meaning: Cortex XDR offers native correlation with Palo Alto firewall data .
12. Cortex XDR WildFire
Example: Perfect when you need integrated sandbox analysis.
Meaning: Cortex XDR includes WildFire sandbox integrated for threat analysis .
Platform Selection Criteria
1. Open, Well-Documented APIs
Example: Use this when evaluating any platform for integration potential.
Meaning: Prioritize platforms with open APIs for ingesting alerts and triggering actions .
2. Interoperability with Existing Stack
Example: Ideal when you need seamless integration with SIEM, EDR, IAM, and ITSM.
Meaning: Look for interoperability with your existing security stack .
3. Automation Readiness
Example: Use this when dashboards aren’t enough and you need action.
Meaning: Prioritize automation readiness, not just dashboards .
4. Flexible Deployment
Example: Perfect for hybrid and multi-cloud environments.
Meaning: Choose platforms that work across hybrid and multi-cloud environments .
5. Data Model Development
Example: Use this when implementing an IRP system.
Meaning: Develop a data model identifying all systems and tools that will interface with the IRP .
6. Playbook Automation Readiness
Example: Ideal when you’re ready to automate response procedures.
Meaning: You cannot just automate a playbook without thorough examination and testing .
7. Terminology Standardization
Example: Use this when implementing incident response platforms across teams.
Meaning: Ensure all project participants are speaking the same language and terms are uniquely identified .
8. Workflow Orchestration
Example: Use this when coordinating technical and business workstreams.
Meaning: The platform should coordinate workstreams with clear owners and escalation paths .
9. Centralized System of Record
Example: Ideal when facts and decisions need to be connected to a consistent incident record.
Meaning: Facts, decisions, tasks, and communications should be connected to a unified record .
10. Dynamic Playbooks
Example: Use this when incident facts and obligations change during response.
Meaning: Workflows should adjust to incident type, severity, and geography .
11. Defensible Documentation
Example: Perfect for compliance-heavy industries.
Meaning: The platform should continuously capture who knew what, when they knew it, and who approved decisions .
12. Readiness and Simulation
Example: Use this when you want to practice with workflows before real incidents occur.
Meaning: The strongest platforms connect planning, tabletop exercises, and live response .
Platform Comparison Insights
1. G2 Grid Leader: KnowBe4 PhishER
Example: Use this when you want the highest-rated incident response platform.
Meaning: PhishER leads the G2 Grid with a 95 score .
2. G2 Market Presence Leader: Datadog
Example: Ideal when market presence matters for vendor stability.
Meaning: Datadog has a 97 market presence score .
3. G2 Satisfaction Leader: PhishER
Example: Use this when satisfaction scores guide your decision.
Meaning: PhishER scores 100 in satisfaction .
4. G2 High Performer: Tines
Example: Perfect when you want strong satisfaction and automation.
Meaning: Tines scores 86 in satisfaction and 58 in market presence .
5. Torq G2 Score
Example: Use this when evaluating automation-focused platforms.
Meaning: Torq scores 70 on the G2 Grid for Incident Response .
6. Cynet G2 Score
Example: Ideal when you want an all-in-one platform with solid reviews.
Meaning: Cynet scores 69 on the G2 Grid .
7. ServiceNow G2 Score
Example: Use this when enterprise workflow integration is key.
Meaning: ServiceNow Security Operations scores 68 on the G2 Grid .
8. Palo Alto Cortex XSIAM G2 Score
Example: Perfect when you’re evaluating ecosystem-integrated platforms.
Meaning: Cortex XSIAM scores 66 on the G2 Grid .
9. CYREBRO G2 Score
Example: Use this when evaluating managed security operations options.
Meaning: CYREBRO scores 65 on the G2 Grid with 93 reviews .
10. Resolver G2 Score
Example: Ideal when centralized tracking and reporting matter.
Meaning: Resolver scores 61 on the G2 Grid .
11. Wazuh vs Splunk Cost Comparison
Example: Use this when budget is a primary concern.
Meaning: Wazuh is free while Splunk costs $130-180/GB/day .
12. Wazuh vs Elastic Migration Time
Example: Perfect when planning a platform migration.
Meaning: Migration from Elastic to Wazuh typically takes 4-8 weeks .
FAQ
What are incident response platforms?
Incident response platforms are software solutions that help security teams detect, investigate, and respond to cybersecurity incidents. They combine capabilities like automation, orchestration, case management, and integration with other security tools .
What’s the difference between SOAR, SIEM, and EDR?
SIEM centralizes and correlates logs for detection. SOAR automates workflows and orchestrates response actions. EDR focuses on endpoint visibility, detection, and containment. Together, they create a coordinated incident response strategy .
Which platform offers the fastest containment?
Cynet, Torq, and Tines are frequently mentioned as fastest containment players for automation-heavy workflows .
Are there free incident response platforms?
Yes. Wazuh is a completely free and open-source option with SIEM and EDR capabilities, compliance integration, and robust FIM .
How long does it take to implement an incident response platform?
Implementation timelines vary. Some platforms like Torq offer agentless automation that deploys in minutes, while enterprise platforms may take months for full integration and workflow development .
Conclusion
Incident response platforms have evolved from simple ticketing systems into powerful automation engines that can contain threats in seconds instead of hours. Whether you choose an automation-first platform like Torq or Tines, an observability-driven option like Dynatrace, or an open-source solution like Wazuh, the key is finding the right fit for your team’s size, budget, and existing stack.
The most important lesson from evaluating these platforms is simple: don’t just buy more tools. Orchestrate them. The value of your incident response capability compounds when your detection and response tools work together seamlessly .
Save this guide for your next platform evaluation. Share it with your security team. And remember, in incident response, speed and coordination aren’t luxuries. They’re requirements.



9 thoughts on “150+ Best Incident Response Platforms for Security Teams in 2026”