
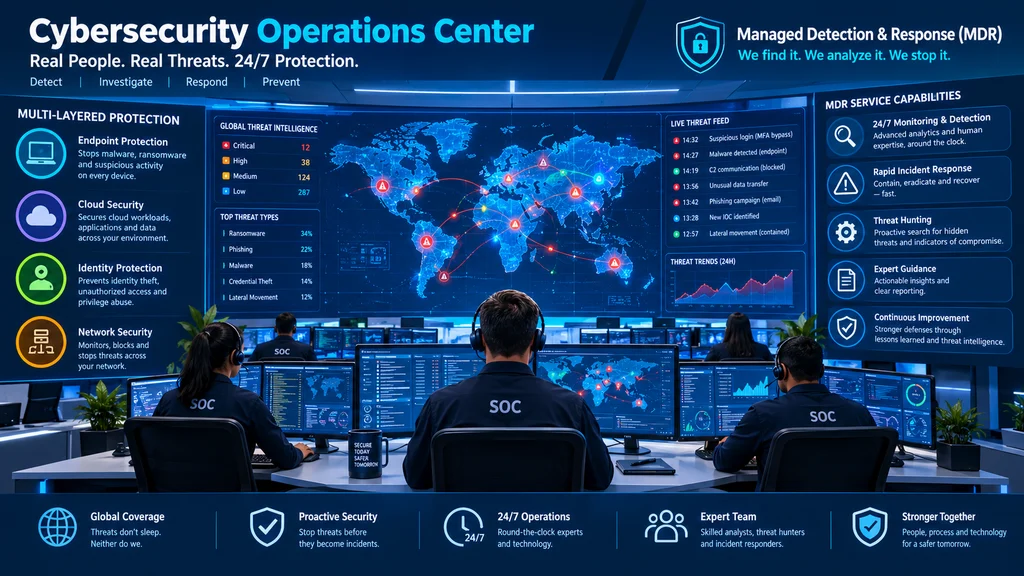
The best managed detection & response provider delivers 24/7 threat monitoring, expert-led incident response, and proactive threat hunting across your entire environment. These services combine advanced technology with human expertise to protect organizations that can’t maintain their own security operations center (SOC). Top alternatives: MDR security service, expert-led threat detection, 24/7 SOC provider, turnkey cybersecurity response, and managed security operations.
Your security team is drowning in alerts. They’re overworked, understaffed, and somehow expected to catch every advanced threat that slips through your firewalls. Sound familiar? You’re not alone. According to industry analysts, 65% of organizations have experienced a significant ransomware event despite major investments in cybersecurity tools .
A managed detection & response provider steps in exactly when you need them most. Instead of trying to build and staff a 24/7 security operations center internally, MDR delivers enterprise-grade protection without the complexity or cost of running it yourself . The right MDR partner acts as an extension of your team, handling everything from threat detection and investigation to active threat containment. Whether you’re a mid-market business or a large enterprise, these services are transforming how organizations defend against sophisticated attacks.
Core Definition Responses
1. MDR provides remotely delivered SOC functions for rapid detection and response
Example: Use this when explaining MDR to non-technical stakeholders.
Meaning: Gartner defines MDR as services that give organizations remote SOC capabilities for threat detection, analysis, and response .
2. MDR combines technology, threat intelligence, and expert analysts
Example: Use this when distinguishing MDR from basic monitoring services.
Meaning: The mandatory features include a shared technology stack, 24/7 staffing, and immediate mitigative response capabilities .
3. MDR offers a turnkey security experience with predefined processes
Example: Use this when comparing MDR to building your own SOC.
Meaning: Providers deliver pretuned detection rules and standard playbooks for efficient operations .
4. MDR covers endpoints, networks, logs, and cloud environments
Example: Use this when describing service scope.
Meaning: Telemetry coverage extends beyond endpoints to include identity, SaaS, and cloud services .
5. MDR analysts hunt for threats proactively, not just reactively
Example: Use this when explaining what makes MDR different from traditional monitoring.
Meaning: Providers use hypothesis-driven threat hunting to identify hidden adversaries before damage occurs .
6. MDR delivers active threat disruption and containment
Example: Use this when discussing response capabilities.
Meaning: Analysts can quarantine hosts and perform other containment actions on your behalf .
7. MDR bridges the cybersecurity skills gap
Example: Use this when explaining the value proposition.
Meaning: Organizations without the staff to run an internal SOC can access expert protection .
8. MDR is outcome-driven security incident management
Example: Use this when focusing on business results.
Meaning: Services are measured by effective detection, investigation, and response outcomes .
9. MDR provides 24/7/365 coverage with follow-the-sun operations
Example: Use this when emphasizing continuous protection.
Meaning: Global SOCs ensure analysts are available around the clock .
10. MDR reduces alert fatigue through intelligent triage
Example: Use this when discussing team productivity.
Meaning: Analysts filter and prioritize alerts so internal teams focus on critical threats .
11. MDR can be vendor-neutral across multiple security tools
Example: Use this when you have existing technology investments.
Meaning: Many providers integrate with third-party security deployments .
12. MDR includes incident tickets with actionable remediation guidance
Example: Use this when explaining what clients receive after an incident.
Meaning: Reports include attack objectives, business impact, and specific remedial actions .
Why Organizations Choose MDR Responses
1. We don’t have the staff to run a 24/7 SOC internally
Example: Use this when explaining why you’re considering MDR.
Meaning: Many organizations lack the security maturity and skill sets for around-the-clock coverage .
2. Our team is overwhelmed by alert volumes
Example: Use this when discussing operational challenges.
Meaning: MDR filters and prioritizes alerts to reduce analyst burnout.
3. We need faster detection and response times
Example: Use this when justifying the investment.
Meaning: Quality MDR providers achieve significantly faster mean time to detect compared to SOC-only operations .
4. Compliance requirements demand advanced security monitoring
Example: Use this when regulatory concerns drive the decision.
Meaning: MDR providers demonstrate compliance through SOC 2 Type II attestations and other certifications .
5. We want to focus internal resources on strategic initiatives
Example: Use this when discussing resource allocation.
Meaning: MDR handles daily operations so teams can work on business priorities .
6. Ransomware attacks are a top concern for our organization
Example: Use this when addressing board-level risk discussions.
Meaning: MDR provides proactive hunting to stop ransomware before encryption occurs .
7. We have a hybrid environment with cloud, endpoint, and on-premises systems
Example: Use this when discussing environment complexity.
Meaning: MDR provides visibility across diverse environments .
8. We need enterprise-grade security but can’t afford a full SOC
Example: Use this when discussing budget constraints.
Meaning: MDR offers cost-effective alternative to building an internal SOC .
9. Our current monitoring tools aren’t delivering desired outcomes
Example: Use this when evaluating current security gaps.
Meaning: MDR helps organizations realize the expected protections from existing security investments .
10. We want expert oversight without the hiring challenge
Example: Use this when struggling to find qualified security talent.
Meaning: MDR gives access to elite analysts without recruiting costs.
11. We need to demonstrate security effectiveness to leadership and customers
Example: Use this when you need to show ROI.
Meaning: MDR provides measurable security outcomes through detailed reporting .
12. We want proactive threat hunting, not just alerting
Example: Use this when seeking active defense.
Meaning: MDR analysts actively hunt for hidden threats, not just wait for alerts to trigger .
Key MDR Provider Features Responses
1. 24/7/365 monitoring across all environments
Example: Use this when evaluating provider coverage.
Meaning: Continuous monitoring is essential for catching threats as they emerge.
2. Mean time to detect (MTTD) under 15 minutes for critical alerts
Example: Use this when comparing performance metrics.
Meaning: Strong providers specify concrete SLAs for triage and response times .
3. Mean time to respond (MTTR) within two hours for containment
Example: Use this when setting expectations.
Meaning: Rapid containment minimizes breach impact.
4. 15-minute triage and 60-minute containment capabilities
Example: Use this when requiring guaranteed response times.
Meaning: Some providers guarantee specific response windows .
5. Integration with existing security tools and firewalls
Example: Use this when you don’t want to rip and replace.
Meaning: MDR providers support existing investments through vendor-neutral approaches .
6. Expanded coverage across identity, cloud, and SaaS applications
Example: Use this when threat actors target multiple entry points.
Meaning: MDR now extends beyond endpoints to identity systems and cloud environments .
7. Access to a global threat intelligence team
Example: Use this when you need real-time threat awareness.
Meaning: Large providers maintain dedicated threat intelligence units .
8. Custom detection engineering beyond vendor signatures
Example: Use this when expecting advanced threat coverage.
Meaning: Mature providers create custom detection rules for your environment .
9. Flexible service tiers based on your organization’s needs
Example: Use this when you want scalability.
Meaning: Providers offer tiers from foundational MDR to full-spectrum MXDR .
10. Transparent service portals with real-time incident status
Example: Use this when demanding visibility.
Meaning: Clients should see incident status, historical trends, and executive-ready reporting .
11. Semi-annual operational efficiency reviews and recommendations
Example: Use this when optimizing your deployment.
Meaning: Some providers offer consultancy insights for ongoing improvement .
12. Incident response retainers for crisis management
Example: Use this when you need extra support during major incidents.
Meaning: Services include annual incident response hours for emergency scenarios .
Vendor-Specific Provider Insights Responses
1. Sophos MDR can operate across Microsoft’s full security suite
Example: Use this when you’re a Microsoft shop.
Meaning: Sophos offers MDR for Microsoft Defender across endpoint, cloud, identity, and Office 365 .
2. Sophos has more than 17,000 MDR customers across all industries
Example: Use this when validating vendor credibility.
Meaning: It’s the most widely used MDR service .
3. Check Point MDR 360 offers vendor-neutral integrations with 160+ tools
Example: Use this when you have heterogeneous security stacks.
Meaning: Check Point’s service works with existing EDR, cloud, firewall, and SaaS tools .
4. Check Point MDR includes native identity threat detection
Example: Use this when identity security is a priority.
Meaning: Native support for Microsoft AD, Entra ID, and Okta is included as a core service .
5. Darktrace MDR combines AI-powered detection with expert analyst oversight
Example: Use this when leveraging AI capabilities.
Meaning: Darktrace’s self-learning AI detects threats while analysts triage and respond .
6. Huntress MDR is designed specifically for mid-market organizations
Example: Use this when you need accessible enterprise-grade security.
Meaning: Huntress provides 24/7 human-led protection at predictable subscription pricing .
7. Bitdefender MDR has 24/7 threat hunting and AI-driven analytics
Example: Use this when you want proactive defense.
Meaning: Their service identifies hidden adversaries before damage occurs .
8. HCLTech MDR uses AI-augmented detection and response at scale
Example: Use this when discussing advanced technology integration.
Meaning: Their Cybervigilia.AI dashboard drives intelligent alert triage .
9. Kudelski Security offers advanced capabilities like managed deception
Example: Use this when you want innovation beyond standard MDR.
Meaning: They use deception technology to force attackers into alternate realities .
10. Unisys MDR leverages AI, automation, and zero-trust principles
Example: Use this when discussing modern security frameworks.
Meaning: Their approach is tailored for hybrid and multicloud environments .
11. Vectra MDR uses AI-driven attack signal intelligence for precision detection
Example: Use this when you need reduced false positives.
Meaning: Their technology minimizes noise and analyst fatigue .
12. Talanos MDR focuses on identity-led detection
Example: Use this when identity is your primary attack vector concern.
Meaning: They monitor identity paths and attacker behavior patterns .
Service Delivery and Operations Responses
1. MDR follows a shared responsibility model between provider and client
Example: Use this when defining working relationships.
Meaning: Clear roles ensure smooth collaboration and effective response .
2. The provider’s platform is host-operated and shared across clients
Example: Use this when asking about the technology model.
Meaning: Telemetry is analyzed within the provider’s own platform .
3. Over 600 providers globally claim to offer MDR services
Example: Use this when discussing vendor selection challenges.
Meaning: Only a select few meet Gartner’s inclusion standards .
4. MDR includes both reactive and proactive incident response
Example: Use this when discussing response types.
Meaning: Services include reactive containment and proactive threat hunting .
5. Providers with global SOCs provide 24/7 coverage year-round
Example: Use this when verifying around-the-clock protection.
Meaning: Follow-the-sun models ensure analyst availability .
6. Service levels include specific SLA commitments with meaningful service credits
Example: Use this when negotiating contracts.
Meaning: Strong providers offer financial accountability for SLA misses .
7. MDR analysts typically hold advanced cybersecurity certifications
Example: Use this when evaluating team expertise.
Meaning: Experience levels and certifications indicate service quality .
8. SOC 2 Type II reports demonstrate effective controls over time
Example: Use this when verifying compliance.
Meaning: Type II shows controls operating effectively over time .
9. Quarterly reviews ensure deployments reach full potential
Example: Use this when expecting ongoing optimization.
Meaning: Regular reviews provide tailored advice on workflows .
10. Service reports provide full transparency on alerts and resolutions
Example: Use this when demanding visibility.
Meaning: Monthly or quarterly reports summarize all activity .
11. Incident response hours can be used flexibly for various scenarios
Example: Use this when discussing retainer value.
Meaning: Hours cover crisis management, tabletop exercises, and compromise assessments .
12. Co-managed models support hybrid in-house and outsourced operations
Example: Use this when you want to maintain some internal control.
Meaning: This model lets organizations choose the right balance for their needs .
Selection Criteria Responses
1. Request actual SLA performance data, not just commitments
Example: Use this when evaluating providers.
Meaning: Demand specific metrics like MTTD and MTTR with verification .
2. Ask about response boundaries and what’s included in the service
Example: Use this to avoid surprise costs or gaps.
Meaning: Clarify exactly where provider responsibility ends .
3. Verify integration support with your existing security tools
Example: Use this when protecting current investments.
Meaning: Check exact log sources supported, not vague assurances .
4. Understand how false positives are managed and tuned
Example: Use this when expecting efficient operations.
Meaning: Providers should discuss false positive rates and tuning methodologies .
5. Confirm 24/7 coverage with multiple global SOCs, not single-location teams
Example: Use this when verifying true 24/7 operations.
Meaning: Single-location teams may struggle with overnight coverage .
6. Demand SOC 2 Type II attestation reports, not Type I
Example: Use this when compliance is critical.
Meaning: Type II demonstrates ongoing control effectiveness .
7. Request a clear explanation of the provider’s detection engineering process
Example: Use this when assessing threat coverage.
Meaning: Custom detection engineering indicates a mature program .
8. Verify compliance certifications relevant to your industry
Example: Use this when regulations apply to you.
Meaning: Healthcare organizations need HITRUST CSF certification .
9. Ask about the provider’s experience with your specific environment size
Example: Use this when you’re a mid-market organization.
Meaning: Some providers specialize in serving mid-sized businesses .
10. Ensure the service aligns with your internal team’s skills and capacity
Example: Use this when defining the engagement model.
Meaning: Services should complement, not overwhelm, your team .
11. Review independent analyst reports and customer peer reviews
Example: Use this when researching providers.
Meaning: Gartner and ISG reports provide independent evaluations .
12. Evaluate the provider’s approach to continuous improvement
Example: Use this when expecting long-term partnership.
Meaning: Regular reviews and optimization indicate commitment to outcomes .
Business Impact Responses
1. Organizations using AI and automation in security save $2.2 million per breach
Example: Use this when building the business case.
Meaning: MDR’s intelligent automation delivers significant cost savings .
2. MDR dramatically reduces breach detection time compared to SOC-only operations
Example: Use this when quantifying speed improvements.
Meaning: Faster detection means lower breach impact .
3. MDR helps organizations achieve faster recovery after incidents
Example: Use this when discussing resilience.
Meaning: Expert guidance accelerates business continuity .
4. MDR improves compliance readiness through documented processes
Example: Use this when regulators are involved.
Meaning: MDR providers demonstrate verifiable controls .
5. MDR reduces the operational burden on internal security teams
Example: Use this when addressing burnout concerns.
Meaning: Offloading alert handling frees staff for strategic work .
6. MDR increases confidence in handling advanced threats like ransomware
Example: Use this when reassuring leadership.
Meaning: Expert coverage provides peace of mind .
7. MDR transforms security from reactive to proactive resilience
Example: Use this when discussing security posture improvement.
Meaning: Proactive hunting prevents attacks before they succeed .
8. MDR provides measurable security outcomes for executive reporting
Example: Use this when demonstrating ROI to leadership.
Meaning: Incident reports translate security metrics to business impact .
9. MDR lowers total cost of ownership compared to building an internal SOC
Example: Use this when discussing budget constraints.
Meaning: Subscription-based pricing eliminates staffing and infrastructure costs .
10. MDR acts as a force multiplier for understaffed security teams
Example: Use this when describing the value proposition.
Meaning: Expert analysts amplify your team’s capabilities .
11. MDR helps retain security staff by reducing alert fatigue and burnout
Example: Use this when addressing retention challenges.
Meaning: Offloading tedious tasks improves job satisfaction .
12. MDR speeds up incident containment and minimizes business disruption
Example: Use this when focusing on business continuity.
Meaning: Rapid response keeps operations running .
Future of MDR Responses
1. MDR is expanding beyond endpoints to identity and cloud
Example: Use this when discussing market evolution.
Meaning: Providers now cover the full enterprise attack surface .
2. Proactive exposure management is becoming a key MDR differentiator
Example: Use this when evaluating provider capabilities.
Meaning: Services increasingly focus on reducing vulnerabilities before exploitation .
3. AI-augmented detection and response capabilities are advancing rapidly
Example: Use this when expecting continuous improvement.
Meaning: AI helps analysts work more efficiently without replacing human judgment .
4. Vendor-neutral MDR options are growing to protect multi-technology environments
Example: Use this when you have diverse security investments.
Meaning: Open platforms integrate with multiple vendors’ tools .
5. MDR providers are adding breach and attack simulation capabilities
Example: Use this when you want continuous security validation.
Meaning: These tools test control effectiveness and identify gaps .
6. Digital forensics and incident response retainers are becoming standard
Example: Use this when expecting comprehensive support.
Meaning: Deep incident investigation is increasingly included .
7. MDR is becoming accessible to mid-market and smaller organizations
Example: Use this when assessing your options.
Meaning: Predictable pricing and simplified deployment make MDR widely available .
8. Compliance alignment is driving MDR adoption across regulated industries
Example: Use this when discussing market drivers.
Meaning: Organizations use MDR to meet regulatory requirements .
9. MDR providers are integrating threat intelligence from multiple sources
Example: Use this when discussing detection capabilities.
Meaning: Broader intelligence improves threat identification .
10. MDR is shifting from alert handling to business outcome delivery
Example: Use this when evaluating service maturity.
Meaning: Focus is on measurable risk reduction, not just alert processing .
11. Co-managed models are growing as organizations want more control
Example: Use this when you want a hybrid approach.
Meaning: Flexibility in management models meets diverse needs .
12. The market is consolidating around providers with proven operational excellence
Example: Use this when vendor selection matters.
Meaning: Established players with track records are preferred .
FAQ
What is a managed detection & response provider?
An MDR provider delivers remotely operated security operations center functions, including threat detection, analysis, investigation, and response. They combine technology, threat intelligence, and expert analysts to protect client environments .
Who needs MDR services?
Any organization that lacks the resources to staff a 24/7 security operations center can benefit from MDR. This includes small to mid-sized businesses and even larger organizations looking to augment internal teams .
How is MDR different from traditional MSSP?
MDR focuses on active threat detection, investigation, and response, while traditional MSSPs often provide passive monitoring and alerting without taking containment actions .
What does an MDR provider actually do?
They monitor your environment 24/7, hunt for threats, triage and investigate alerts, and perform containment actions like quarantining compromised hosts. They provide incident reports and recommend remediation steps.
How do I choose the right MDR provider?
Evaluate their integration support, SLA performance data, team expertise, compliance certifications, and operational transparency. Request specific metrics and verify their approach to detection engineering .
Conclusion
A managed detection & response provider could be the best investment you make for your organization’s security. The gap between sophisticated threats and available security talent continues to widen, and MDR services bridge that gap.
The right provider doesn’t just monitor your environment for threats. They hunt proactively, respond decisively, and act as a true extension of your team. They reduce alert fatigue and free up internal resources for strategic priorities .
When evaluating MDR providers, demand transparency on performance metrics, integrations, compliance certifications, and response boundaries. The best providers deliver measurable security outcomes that go far beyond just telling you what’s happening. They actively defend your organization with elite experts who work 24/7 on your behalf.



5 thoughts on “150+ Best Managed Detection & Response Provider Insights for Cybersecurity Leaders For 2026”